A structured project risk assessment checklist gives engineering and construction teams an audit-ready risk register, scored risks with named owners, documented mitigation actions, and a defined review cadence — all aligned to U.S. statutory compliance requirements for building projects. Run this process at pre-bid, design stage, pre-construction, and each project stage gate. Structured risk assessment is not optional on U.S. building projects; it is the mechanism by which permit delays, code non-conformance, and site-safety failures are identified before they become schedule or cost events.
TL;DR — Core anchors this checklist uses:
- APM risk-management stages (analysis → evaluation → mitigation) for scoring governance
- ISO 31010-style likelihood × impact scoring (1–5 scale) with defined appetite thresholds
- OSHA, ADA, and IBC statutory checkpoints captured as discrete register entries
Copyable checklist for a project brief:
- Define scope, constraints, and risk appetite thresholds
- Identify risks by category (financial, legal, environmental, safety, technical)
- Score each risk: likelihood (1–5) × impact (1–5) = raw rating
- Assign a named owner and mitigation action per risk
- Set residual score target and mitigation deadline
- Record statutory compliance checkpoints (permits, OSHA, ADA, fire/egress)
- Schedule review cadence (weekly/monthly/stage-gate)
- Populate the risk register and distribute to the project team
Table of Contents
- What does a full project risk assessment checklist cover?
- How do you score risks and prioritize them?
- How should you assign owners, mitigation actions, and review cycles?
- Which U.S. statutory checkpoints must appear in the checklist?
- What does a risk register template look like for building projects?
- How do you embed risk assessment into project governance and procurement?
- Key Takeaways
- Why the checklist matters more than the scoring system
- Aman Engineering Consultancy delivers compliance-ready risk assessments
- Authoritative sources and further reading
What does a full project risk assessment checklist cover?
A risk management checklist for building projects follows a structured sequence: identify threats, score likelihood and impact, determine a risk rating, assign a named owner, develop mitigation strategies, and set recurring monitoring cycles. Each step produces a discrete, auditable output. The sequence below is operational — project teams can follow it without additional interpretation.
Minimum evidence required per risk entry:
- Trigger event or condition that activates the risk
- Key risk indicator (KRI) used to monitor onset
- Assumed probability band and impact band (cost, schedule, or performance)
- Regulatory reference where a statutory obligation applies
- Supporting documents (geotechnical report, permit application, inspection record)
- Assigned owner name and contact
RACI example for a five-person project team:
| Action | Project Manager | Discipline Lead | Compliance Officer | Contractor |
|---|---|---|---|---|
| Identify risks | A | R | C | C |
| Score risks | R | C | C | I |
| Assign mitigation | A | R | C | R |
| Review register | R | C | R | I |
R = Responsible, A = Accountable, C = Consulted, I = Informed
Early multi-discipline workshops and documented lessons learned reduce the chance of missing site-specific or asset-specific hazards — a consistent failure mode on complex construction projects.
How do you score risks and prioritize them?
The 1–5 likelihood and impact scales
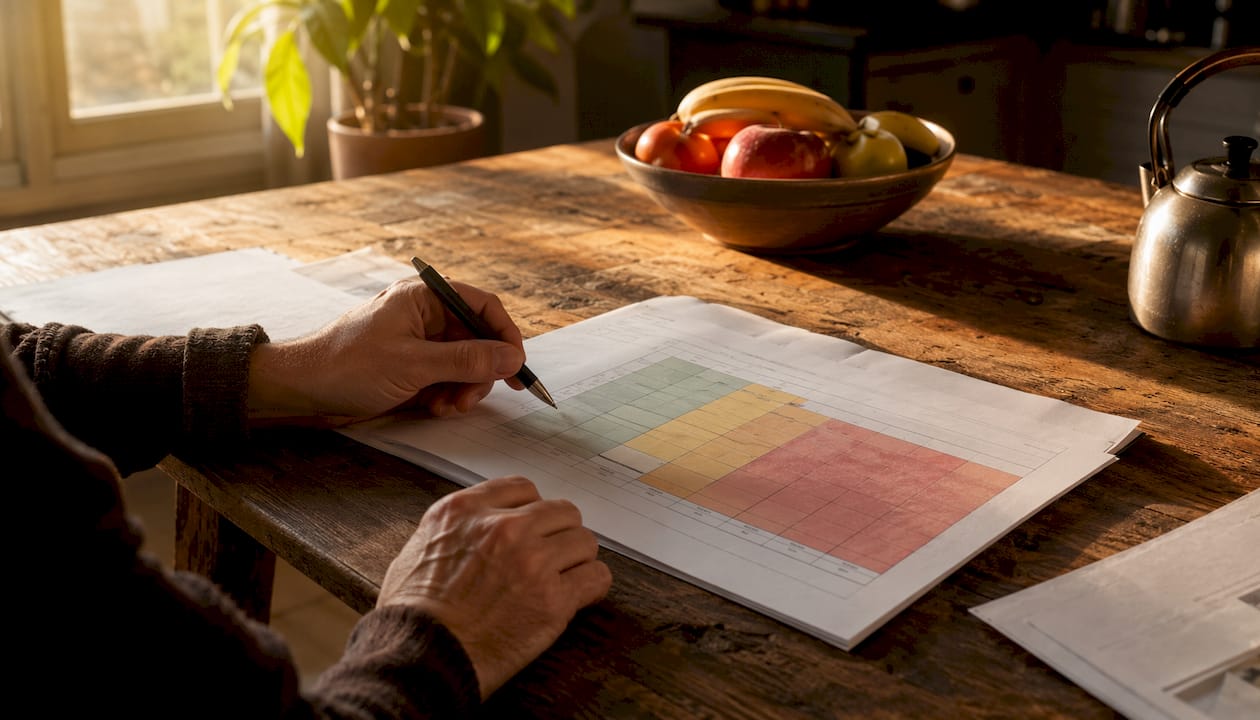
Score likelihood on a 1–5 scale from rare to almost certain. Score impact on a parallel 1–5 scale tied to defined thresholds from negligible to critical. Multiply the two scores to produce the raw risk rating.
5×5 risk matrix with traffic-light thresholds
| Impact → | 1 Negligible | 2 Minor | 3 Moderate | 4 Major | 5 Critical |
|---|---|---|---|---|---|
| 5 Almost certain | 5 | — | 15 | 20 | 25 |
| 4 Likely | 4 | 8 | 12 | 16 | 20 |
| 3 Possible | 3 | 6 | — | 12 | 15 |
| 2 Unlikely | 2 | 4 | 6 | 8 | — |
| 1 Rare | 1 | 2 | 3 | 4 | 5 |
Green: 1–5 (monitor). Amber: 6–14 (active management). Red: 15–25 (escalate immediately).
Treat any risk scoring 16 or above as requiring immediate escalation and a documented response plan. APM guidance defines two primary stages: risk analysis (estimating and evaluating) and risk management (mitigating), using qualitative techniques for quick overviews and quantitative techniques for high-priority risks.
Expected Monetary Value and quantitative escalation
For a cost risk example, use the Expected Monetary Value (EMV) method by multiplying the probability by the estimated cost impact; this figure informs the project contingency budget. When multiple high-scoring risks interact, or when the EMV calculation relies on uncertain probability estimates, escalate to Monte Carlo simulation or sensitivity analysis. Qualitative methods scope and prioritize; quantitative methods provide decision-grade precision for the highest-exposure items.
Pro Tip: Check for two common scoring biases before finalizing ratings. Single-score obsession occurs when teams assign one probability figure without testing the range; velocity bias occurs when teams ignore how quickly a risk could materialize. A risk with a score of 12 that can escalate to a score of 20 within two weeks demands the same urgency as a risk already rated 16.
A rigorous evaluation step compares quantified exposure against defined appetite thresholds to drive treatment decisions. Without those thresholds, a register lists observations rather than producing escalation decisions.
How should you assign owners, mitigation actions, and review cycles?
Ownership and monitoring are where most risk registers fail. Each risk row must carry a named individual, not a role title, as the accountable owner. The following sequence applies to every risk rated amber or red.
- Assign the named owner. Record full name, role, and direct contact. The owner is accountable for the mitigation action and the review date.
- Define the mitigation action. State the specific action (not a category), the budget code if expenditure is required, and the expected reduction in likelihood or impact.
- Set the mitigation deadline. Tie the deadline to a project milestone or stage gate, not a calendar date alone.
- Record the residual score. After the mitigation action is complete, re-score likelihood and impact. The residual score must fall within the project’s defined risk tolerance.
- Set the review date. Weekly during construction-critical phases; monthly during design; triggered at every stage gate and at any change-control event.
Review cadence triggers: a change-control submission, a permit decision, a design revision, a contractor substitution, or any KRI breach. Continuous monitoring, stage-gate reviews, and lessons-learned integration turn a one-off assessment into a living risk control process. Risk registers should include review dates, owners, and residual risk fields to remain actionable throughout the project lifecycle.
Which U.S. statutory checkpoints must appear in the checklist?
For U.S. building projects, statutory risks must be captured as discrete register entries, each with a regulatory reference, required deliverable, named owner, and deadline. Missing a single permit or code checkpoint can halt construction and trigger enforcement action.
Statutory compliance is not a background condition — it is a category of project risk. Each permit, code section, and agency approval carries a probability of delay or rejection that must be scored, owned, and monitored with the same discipline as cost or schedule risks. Capturing these items as discrete register entries makes mitigation traceable and audit-ready.
Mandatory statutory checkpoints for U.S. building projects:
- Building permit and plan review: local authority jurisdiction, plan examiner comments, resubmission cycles
- International Building Code (IBC) compliance: occupancy classification, structural loads, means of egress
- Fire and egress: NFPA 101 Life Safety Code, sprinkler system design, fire-rated assemblies; see also fire-risk and egress guidance for site-specific considerations
- OSHA site-safety plan: 29 CFR 1926 Construction Standards, fall protection, excavation safety, hazard communication
- ADA accessibility: ADA Standards for Accessible Design, accessible routes, parking, restroom compliance
- Environmental permits: Clean Water Act Section 404, stormwater pollution prevention plan (SWPPP), local wetlands review
- Utility coordination: underground utility locates, utility company approvals, service connection permits
- Municipality-specific approvals: zoning variances, historic preservation review, traffic impact studies
Record each checkpoint as a risk entry with the triggering condition (e.g., “plan examiner issues major correction”), the regulatory reference (e.g., IBC Section 1006), the required deliverable (revised drawings), the owner (architect of record), and the deadline (resubmission within 21 days of comment). Professional engineers managing statutory submissions track these items against the permit timeline to prevent approval delays from compressing the construction schedule.
What does a risk register template look like for building projects?
The table below is a fillable template. Copy the column structure into your project-controls system or export as CSV. Each row represents one discrete risk.
| Risk ID | Category | Description | Likelihood (1–5) | Impact (1–5) | Raw Score | Mitigation Action | Owner | Mitigation Owner | Deadline | Residual Score | Review Date | Evidence Link |
|---|---|---|---|---|---|---|---|---|---|---|---|---|
| R-1 | Schedule | Long-lead M&E equipment delayed by 8 weeks due to supply-chain disruption | 4 | 4 | 16 | Place purchase order 16 weeks before required on-site date; identify alternate supplier | PM | M&E Lead | Per procurement schedule | 6 | Monthly / stage gate | PO log, supplier lead-time confirmation |
| R-2 | Technical | Unforeseen subsurface conditions require redesign of foundation system | 3 | 5 | 15 | Commission geotechnical investigation before design freeze; include contingency sum ($100,000 EMV) | Structural Lead | Geotechnical Consultant | Prior to design freeze | 6 | At design stage gate | Geotech report, foundation design revision |
| R-003 | Statutory | Building permit plan review exceeds baseline duration, delaying construction start | 3 | 4 | 12 | Submit complete permit package well before planned construction start; assign permit expediter | Compliance Officer | Architect of Record | Pre-construction | 4 | Weekly during permit review | Permit application, examiner correspondence |
For import into common project-control platforms, map columns as follows: Risk ID → issue key, Raw Score → priority field, Owner → assignee, Review Date → due date. Risk assessment registers maintained by the consultancy follow this column structure and are available as downloadable templates.
How do you embed risk assessment into project governance and procurement?
Risk assessment produces value only when it is connected to the decisions that govern cost, schedule, and scope. Three integration patterns make the register operational rather than archival.
Link risk entries to change control. Every change-control submission should reference the risk ID it activates or closes. A scope change that increases the probability of a permit delay should trigger an immediate re-score of R-003 and a revised mitigation deadline.
Connect contingency budgets to EMV totals. Sum the EMV figures for all red-rated risks and verify that the project contingency fund covers at least that exposure. When the contingency falls short, escalate to the project sponsor before the next stage gate.
Tie risk IDs to CPM schedule windows and BIM issues. In scheduling software, tag float-critical activities with the risk IDs that threaten them. In BIM coordination, log clash-detection issues against the relevant risk entry so that resolution closes the risk rather than creating an orphaned action item. Construction project-controls platforms increasingly support direct linking between risk registers and BIM issue trackers, reducing the manual effort required to keep both systems synchronized.
Pro Tip: Use historical project data from completed projects of similar type and scale to seed the initial risk identification workshop. A practitioner checklist drawn from past projects surfaces site- or asset-specific hazards that generic category lists miss. Wharton’s risk-management guidance recommends using dashboards with key risk indicators and regularly questioning whether monitoring coverage is sufficient — a discipline that prevents the register from becoming static.
For construction project planning, integrating risk review dates with the master program schedule ensures that no stage gate passes without a current, signed-off register.
Key Takeaways
A structured project risk assessment checklist, applied at each project stage gate, produces an audit-ready register with scored risks, named owners, mitigation actions, and statutory compliance checkpoints that support U.S. building permit and code approval processes.
| Point | Details |
|---|---|
| Score every risk consistently | Use likelihood × impact (1–5 × 1–5); escalate any risk scoring 16 or above immediately. |
| Capture statutory items as risks | Record each permit, code section, and agency approval as a discrete register entry with owner and deadline. |
| Assign named owners, not roles | Each risk row requires a named individual accountable for the mitigation action and review date. |
| Keep the register live | Update residual scores after mitigation; trigger re-scores at every change-control event and stage gate. |
| Aman Engineering Consultancy | Delivers full risk register population, mitigation planning, and statutory submission support for U.S. building projects. |
Why the checklist matters more than the scoring system
The most common failure in project risk management is not a flawed scoring formula. It is a register that is populated once at project kickoff and never updated. A risk rated 8 at design stage can reach 20 by the time structural steel is being erected, if no one has reviewed it against the evolving site conditions, permit status, and procurement lead times. The scoring system is a tool; the discipline of review is the actual risk control.
A second underappreciated point: statutory compliance risks are routinely treated as administrative tasks rather than project risks. A permit delay of 30 days on a critical-path activity carries the same schedule exposure as a contractor default. Capturing it in the register, assigning an owner, and tracking it weekly gives the project team the same visibility and response capability they apply to cost and schedule risks.
The checklist in this article is designed to close both gaps: it forces a review cadence and it requires statutory checkpoints to be entered as scored, owned register entries.
Aman Engineering Consultancy delivers compliance-ready risk assessments
Aman Engineering Consultancy provides end-to-end risk assessment services for U.S. building projects, from initial register population through statutory submission support. Project owners and developers who need an audit-ready deliverable — not just a spreadsheet — can engage Aman to deliver the full scope.
Typical deliverables include:
- Populated risk register with scored risks, named owners, and mitigation actions
- Statutory compliance checkpoint mapping (permits, OSHA, ADA, IBC, environmental)
- KRI dashboard configured to the project’s review cadence
- Mitigation plan with EMV calculations and contingency budget alignment
- BIM/project-controls integration support
To commission a risk assessment or discuss statutory submission requirements for your project, contact Aman Engineering Consultancy directly. Teams that need guidance on engaging engineering consultants for assessment delivery will find scope and fee structure guidance on the Aman website.
Authoritative sources and further reading
For audit documentation: cite APM PRAM for scoring governance, ISO 31010 for evaluation methodology, and the relevant OSHA standard (29 CFR 1926) or IBC section for each statutory checkpoint. These references give compliance reviewers a traceable basis for every scoring decision in the register.
Core references used to form this checklist:
- APM Project Risk Analysis and Management (PRAM): primary authority for risk analysis and management stages, qualitative vs. quantitative technique selection
- Galorath Risk Evaluation guidance: defines the distinction between risk analysis and risk evaluation; source for appetite-threshold methodology
- Atlassian Risk Analysis in Project Management: practical five-step process for teams using project-management software; useful for tool-integration workflows
- SafetyCulture Risk Management Checklist: register field requirements, review-date discipline, and residual-risk tracking
- OSHA 29 CFR 1926 Construction Standards: authoritative source for all site-safety statutory checkpoints
- ADA Standards for Accessible Design: authoritative source for accessibility compliance entries
- International Building Code (IBC): authoritative source for occupancy, egress, and structural compliance entries
- Wharton Managing Risk: A Checklist for Leaders: governance and dashboard discipline for embedding risk management into project management routines
- Minnesota DOT Project Risk Checklist: practitioner-level checklist for stakeholder workshop facilitation and lessons-learned integration